Creating the modern workplace! – Vision
- Increase mobility: People are working from home. From clients and during travel. In regard to collaboration, 98% of information workers collaborate or communicate with someone else at work on a weekly basis.
- Improve security and compliance. Most of the time there is no control of data compliance in the current on-premise environment. Security systems are complex and static without growing or proven improvements.
- Start with a Zero Trust model. Start with protection of your people.
What is Multi-Factor Authentication – To know
- Something you know, typically a password or a pin-code.
- Something you have, such as a trusted device that is not easily duplicated, like a phone or hardware key/token.
- Something you are – biometrics like a fingerprint or face scan.
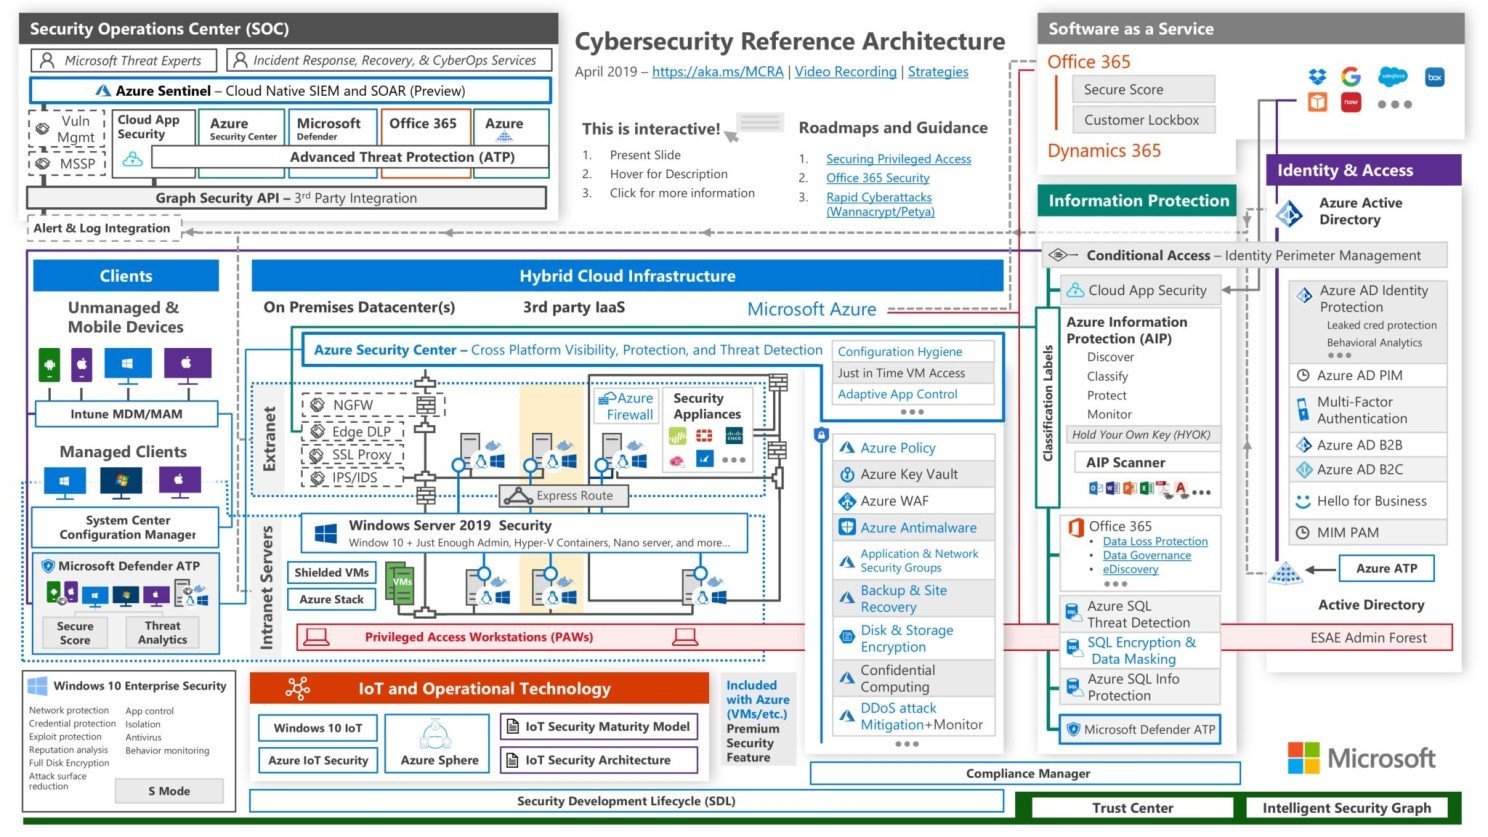
Cybersecurity Reference Architecture – Deep integration for future secops
I think we need to see and understand that the small parts (Micro) are connected to the big parts. (Macro) Identity & Access management is crucial. Identity is the first step. It is the baseline to configure well. Next to the macro view of this Cybersecurity Reference architecture we need to dare to question the identity providers we have integrated in our current environment.
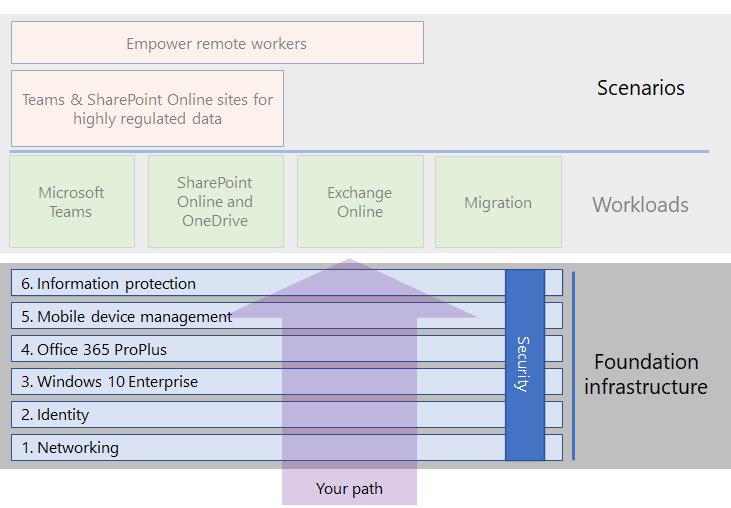
Foundation Infrastructure – The not so interesting part
Starting with your foundation.
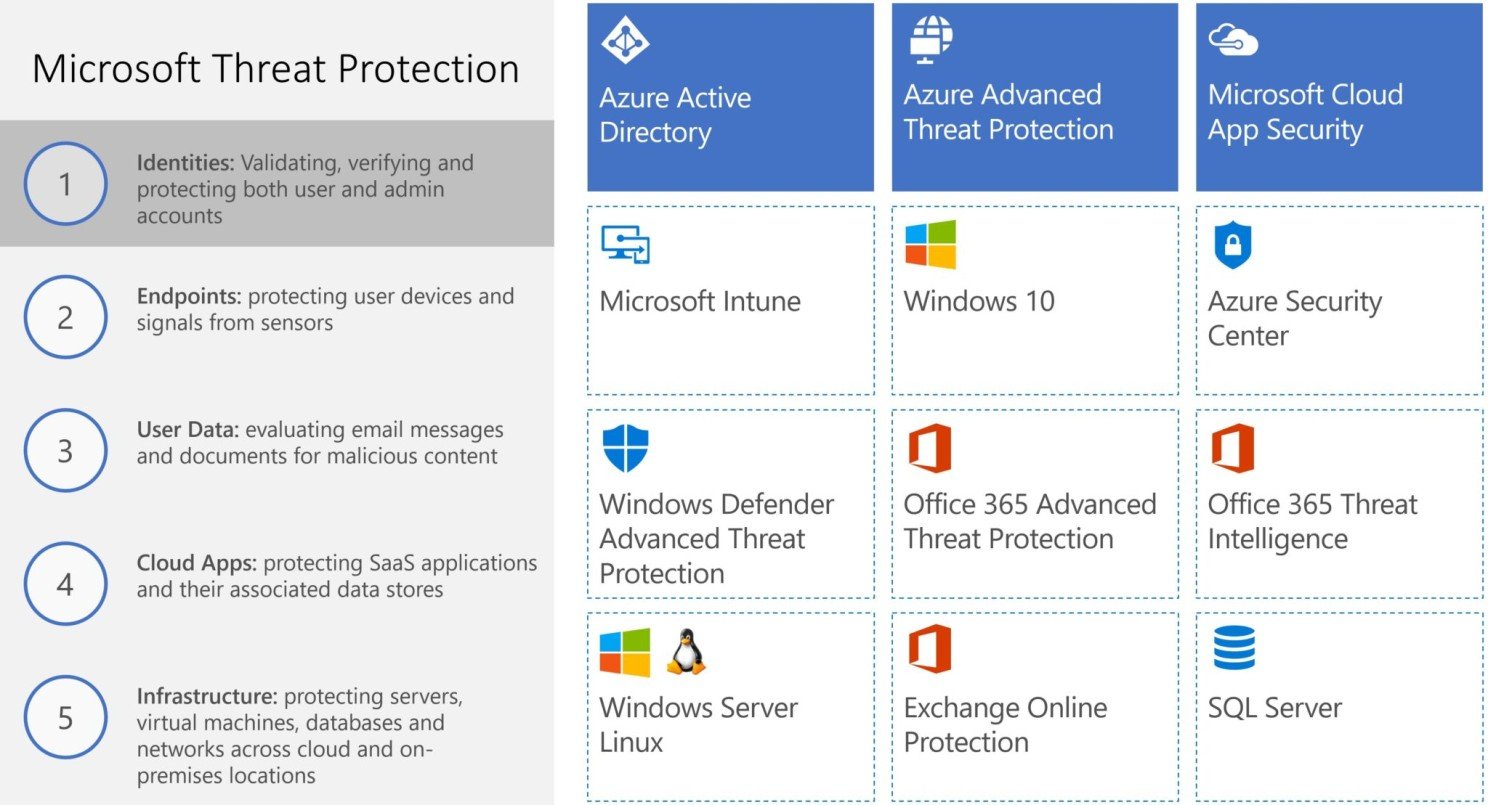
Identity is a fundamental part of the workplace – The attack surface
As you can see in this figure all security mechanisms are built on the fundamentals of Identity Management. What can you protect IF you're not able to enable MFA? It has its reasons. There are numbers out there to make you aware of this. We will come to that, later in this article.
Cloud Architecture Identity – MFA is part of something
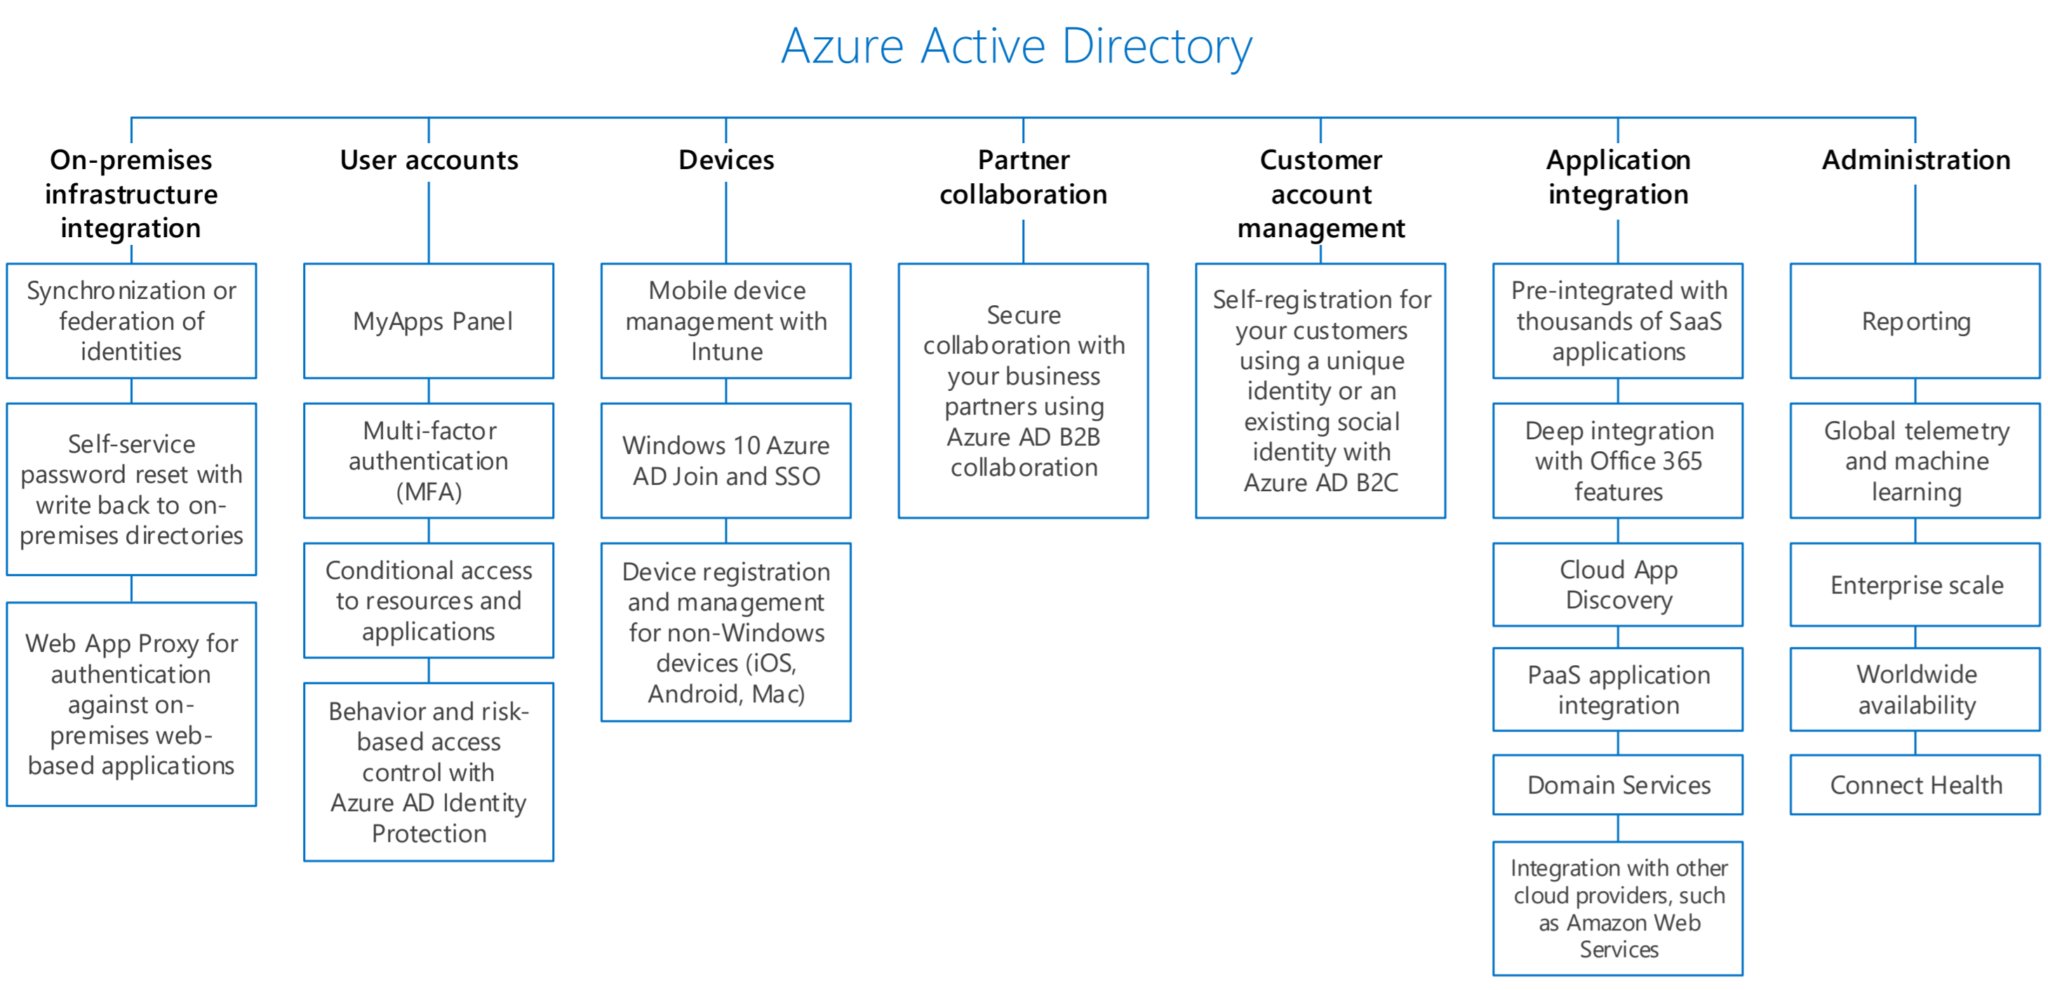
Understanding identity management in the eco-system of Microsoft's Identity management system is crucial to find the place where Multi-factor authentication (MFA) belongs.
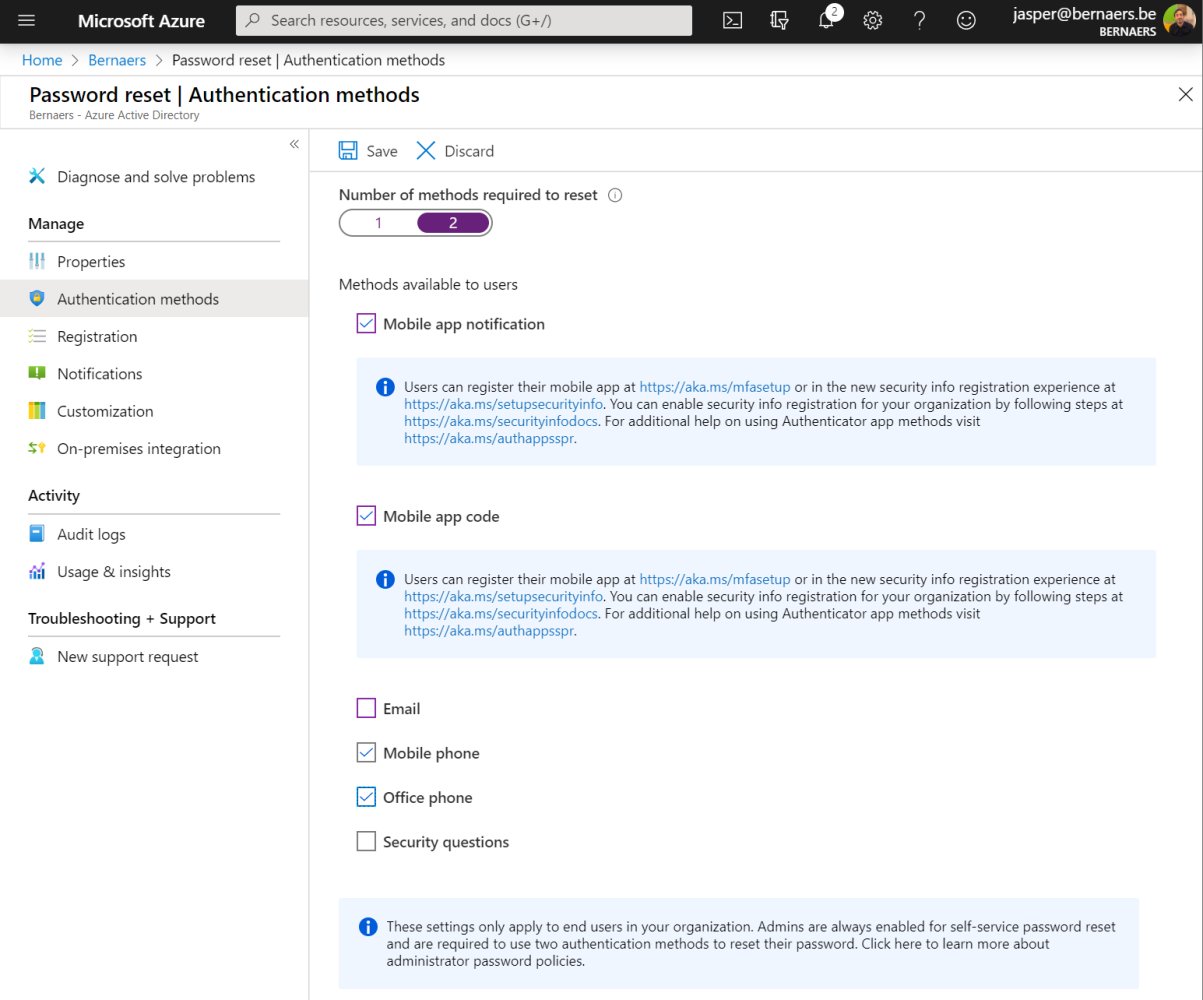
Self-Service Password Reset – To help the people getting less frustrated when having Password problems
Give people in your organization the ability to get some advantages because they 'need' to do MFA. This will ask people of your organization to change their password when there is a threshold higher or above the risk level. It will decrease the IT workload and more importantly it will make your customers happy.
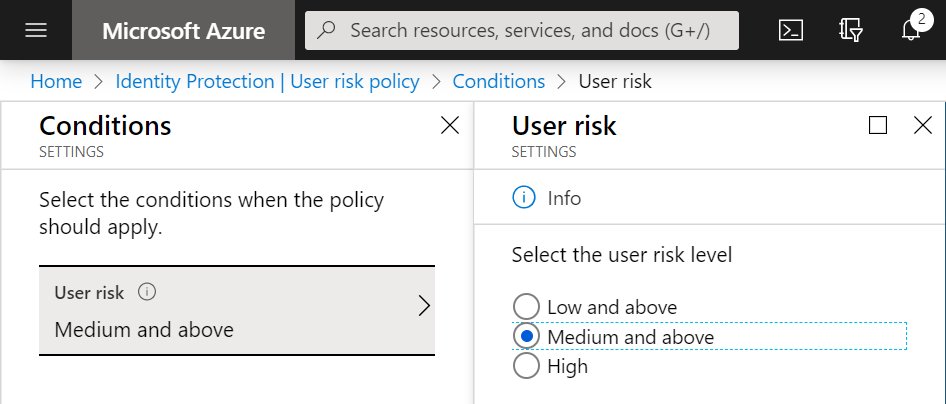
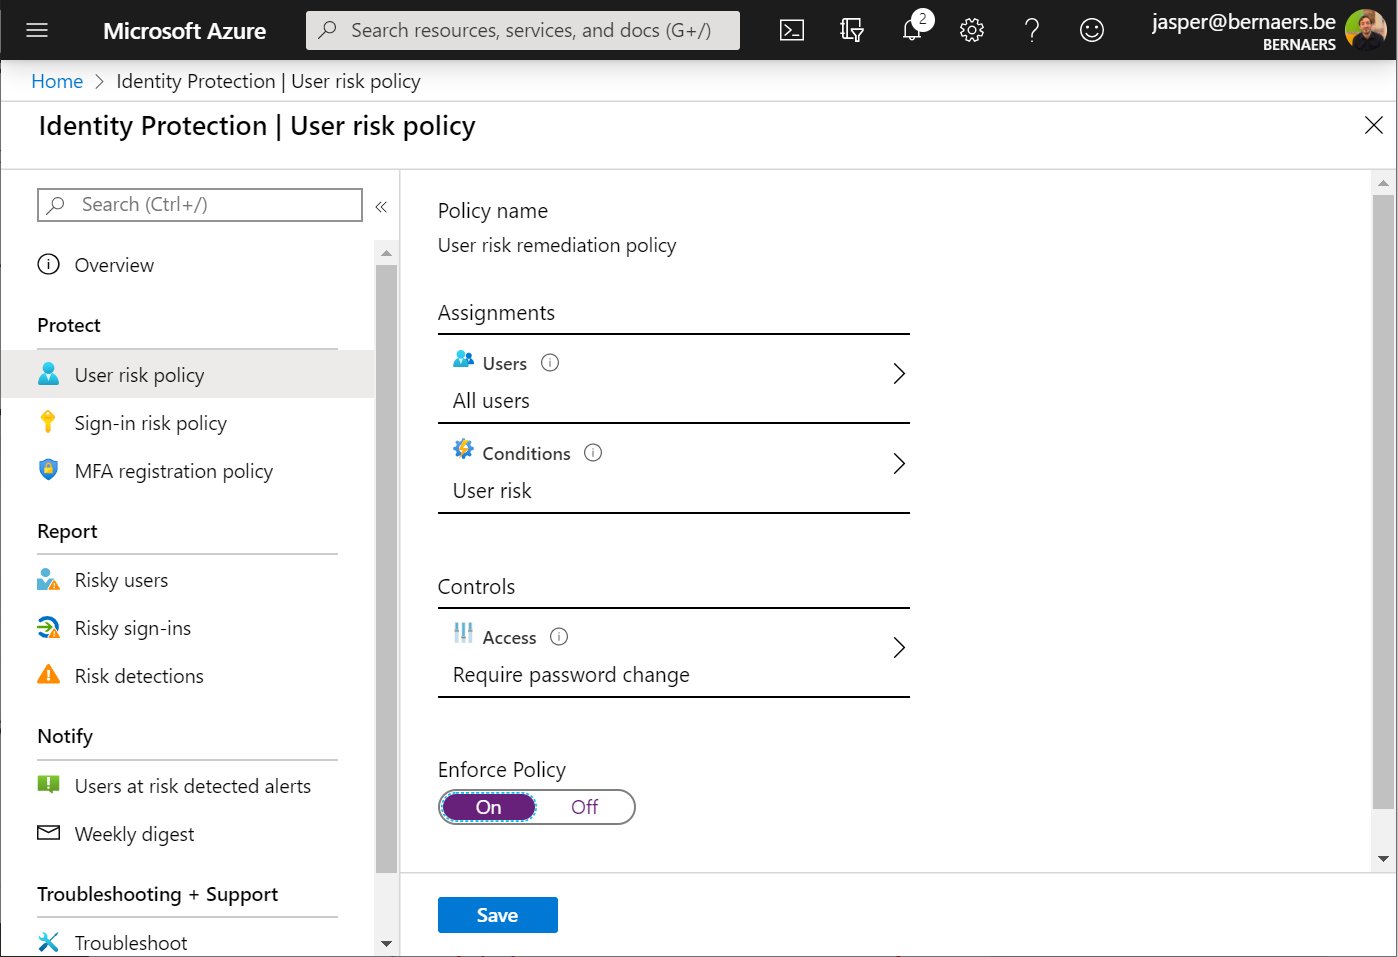
Force a password change when assuming breach – To prevent breaches AND decrease IT tickets
Go to Identity Protection in Microsoft Azure. Select your assignment. All users. Conditions. Select your requirement. And select Require Password Change. This will ask people of this organization to change their password when the threshold is at or above the risk level.
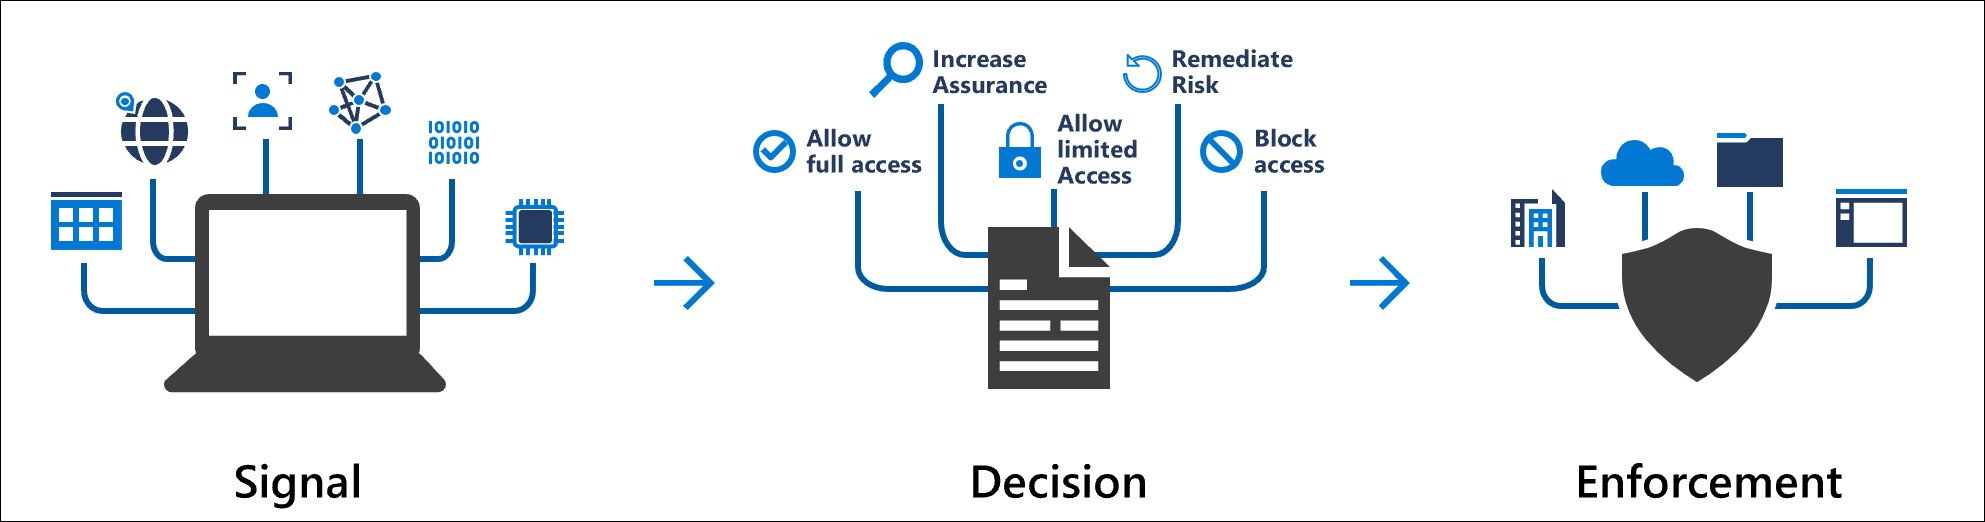
Azure AD Conditional Access – To make it easier
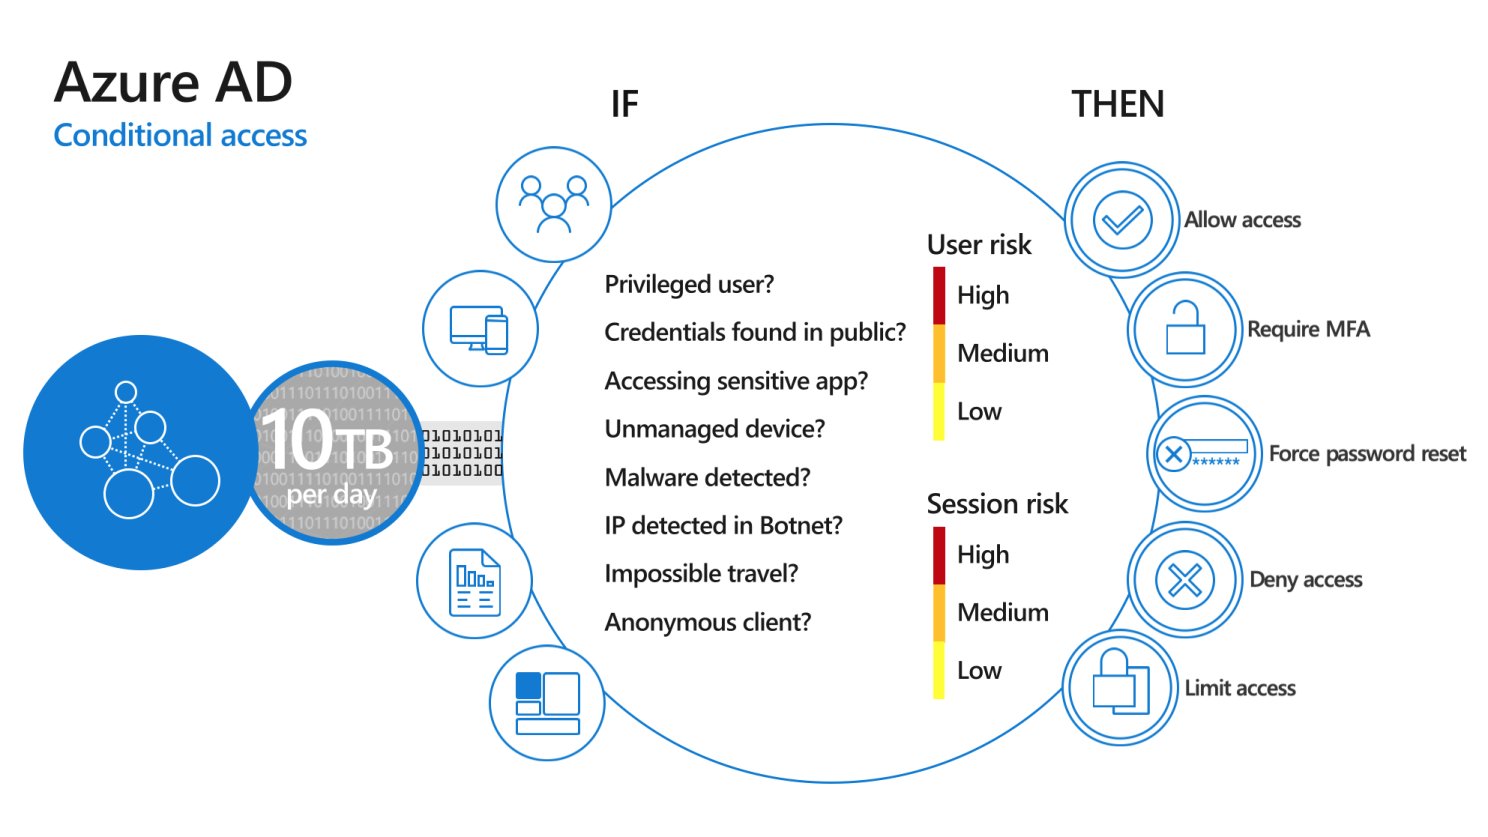
Conditional Access is a solution used by Azure Active Directory to bring signals together, to make decisions, and enforce organizational policies. Conditional Access is at the heart of the new identity driven control plane.
- Keep user accounts safe by requiring strong authentication based on location and risks.
- Keep data safe by only allowing managed devices.
- Meet compliance requirements.
- Create simple policies for everyone – not for groups, departments – make it simple!
Your modular dreams…
What if MFA fails like it did before? – Probably won't
MFA failed 2 times? Less than 4 hours? Ever? Compared to your on-premise environment? We like to kill MFA implementations because we don't like it but we still want more security. DO IT. If security is a priority, you can fix this technically. What if that's the real problem? What if you did not have MFA and are breached? OR leave MFA enabled and still be in control of your data.
What if MFA failed and you had your devices and identities connected to your modern workplace because it was not a side-project and part of a strategic decision — and were able to work when the service fails for some hours?
- High risk users will get unique passwords.
- Low risk users may authenticate without password change.
- Risky users with medium risk and higher will get a password change.
The standard pitch of factual motivation
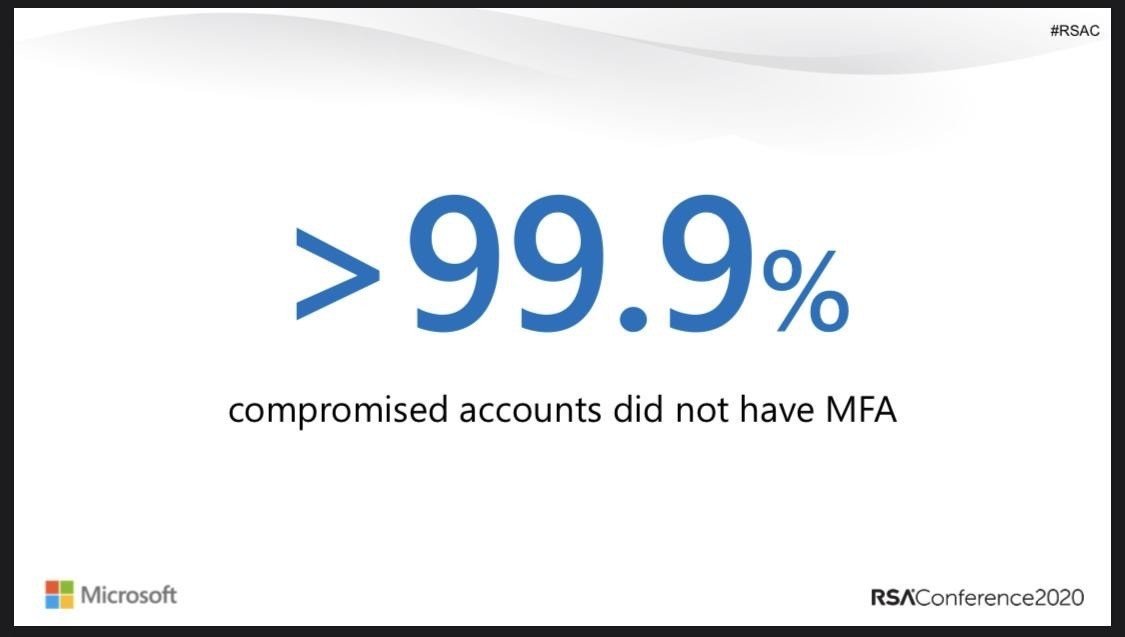
For me it has always been a big challenge to pitch the facts when it comes to activation or enrolling of MFA. Still these are the valid statistics and elevator pitches about single password, compromised accounts…
"Any fool can know, the point is to understand."— Albert Einstein
Passwordless authentication – To give people a great advantage
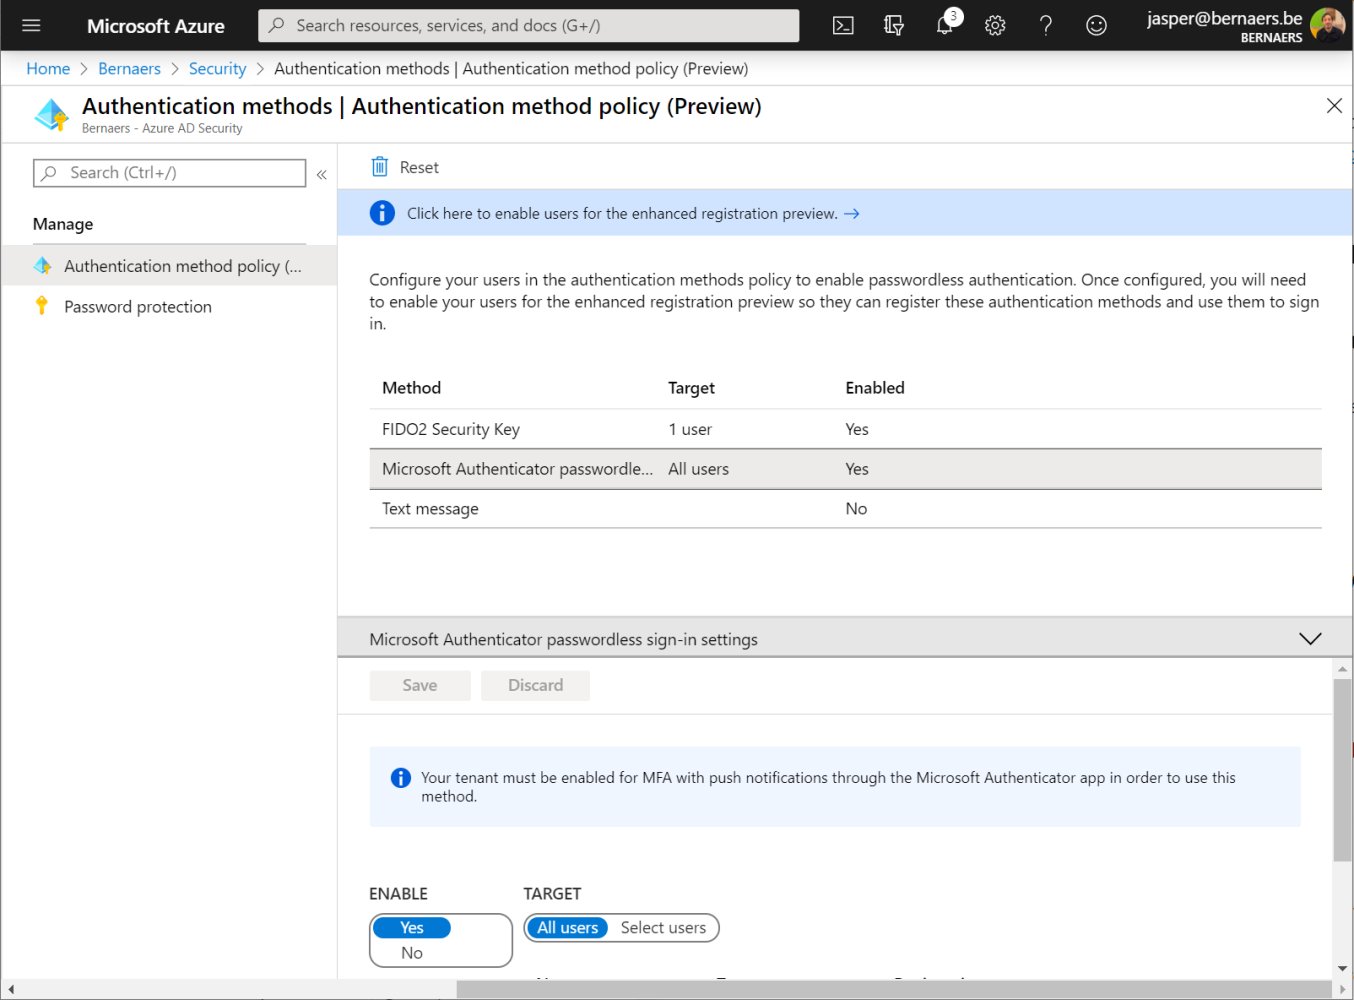
Enablement of Passwordless authentication will activate authentication without a password – isn't this great? Enablement of password Authentication in Azure AD is easy.
Passwordless authentication is a feature that lets us rethink our current MFA solution IF it's not running in the cloud or third-party. As you can see the integration is deeper and deeper here.
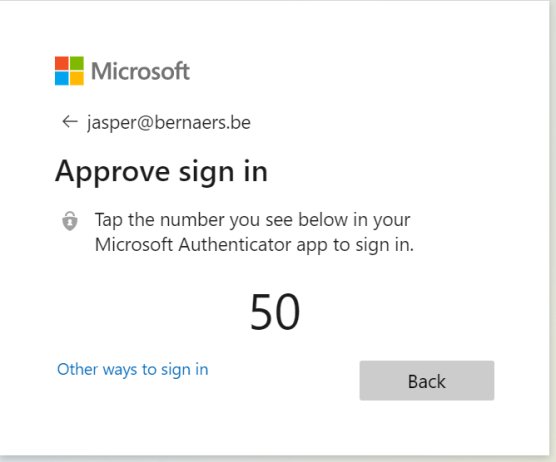
The MFA Experience – It isn't bad at all
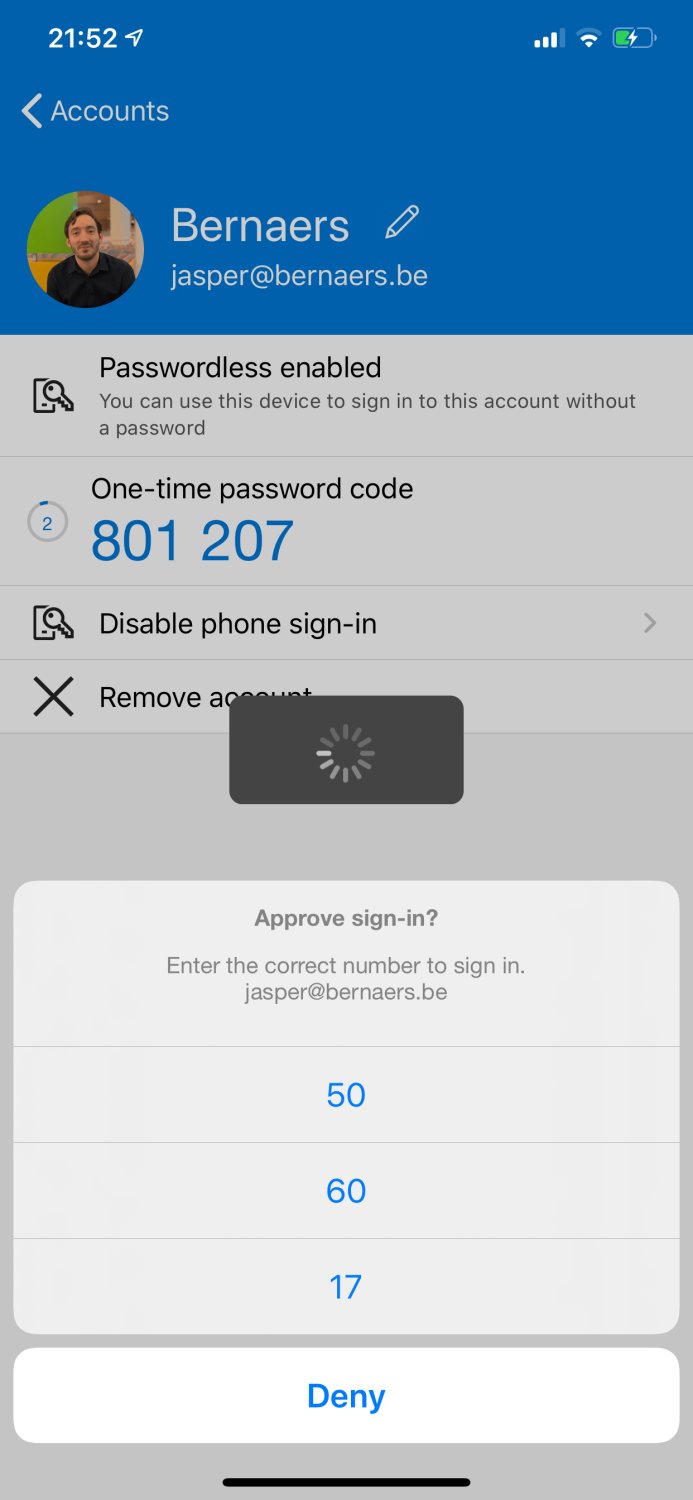
The mobile experience shows 3 sign-in codes to validate the sign-in. Your code needs to be validated — and you don't need to enter the password.
Combined MFA and password reset registration – To make the onboarding smooth
Microsoft has announced that the combined security information registration is now generally available (GA). This new experience makes it easy for users to register for Multi-Factor Authentication (MFA) and Self-Service Password Reset (SSPR) in a simple step-by-step process.
Adoption and change management – To make everyone happy and included
- Make standards that are understandable for everyone, not only for the IT organization.
- Communicate MFA announcement and changes before the change – not after.
- Keep track of the change record.
- Explain very well how you're using 'standards' in your organization.
- Put the guidelines on a place where all procedures are located.
- Communicate over multiple platforms.
- Make it about the end-user.
- Help end-users.
❯ Frequently Asked Questions
Frequently Asked Questions
What are the three factors used in multi-factor authentication?
Something you know — a password or PIN; something you have — a trusted device such as a phone or hardware key; and something you are — biometrics like a fingerprint or face scan.
How do I enable MFA for my organization in Azure AD?
The fastest path is Azure AD security defaults, which push MFA to every account and disable legacy authentication that doesn't support MFA. For more granular control, use Conditional Access policies instead.
What's the difference between security defaults and Conditional Access for MFA?
Security defaults is an all-or-nothing switch — MFA for everyone, no exceptions. Conditional Access lets you build IF/THEN policies based on signals like user risk, location, and session risk, so you can require MFA only in specific conditions rather than universally.
What percentage of compromised accounts didn't have MFA enabled?
More than 99.9% of compromised accounts had no MFA enabled, according to Microsoft. That single statistic is the strongest argument for turning it on everywhere.
Is MFA included in my Microsoft 365 or Office 365 license?
Yes — basic MFA is included in all Office 365 and Microsoft 365 licenses. It doesn't include Conditional Access or some of the other features described here, which require Azure AD Premium.
What is Self-Service Password Reset (SSPR) and why does it matter?
SSPR lets users reset their own password when a risk threshold is crossed, without opening an IT ticket. Configure it under Azure AD → Password Reset → Authentication Methods. It reduces IT workload and gets frustrated users back to work faster.
What happens if a user's account is flagged as high risk?
Depending on your Identity Protection policy, high-risk users can be required to change their password immediately, while lower-risk users may authenticate without a change, so you can scale the response to the actual level of risk.
What is passwordless authentication and how do I turn it on?
Passwordless authentication lets users sign in without ever entering a password, using a FIDO2 security key, Microsoft Authenticator, or a text message. Enable it under Azure Active Directory → Security → Authentication methods → Authentication method policy.
What should I do if MFA fails or locks someone out?
Keep a break-glass emergency access account excluded from your Conditional Access policies for exactly this situation, and write a short internal document describing what to do when someone can't complete MFA.
How do I roll out MFA without a wave of help-desk tickets?
Communicate the change before it happens, not after; use the combined MFA and SSPR registration experience so users set up both in one simple step; and put clear guidance wherever your other IT procedures already live.
Do I need Conditional Access to require MFA, or is security defaults enough?
Security defaults is enough to require MFA for everyone with zero configuration. Conditional Access is worth the extra setup once you need exceptions — trusted locations, compliant-device requirements, or different rules for admins versus regular users.